Black Friday 2026 · 5 deals from €500, up to 61% off · ends in Android Kernel + Userland: + 3 months of Djini.ai Research (worth €750) · 48-hour bonus ends in --
Black Friday 2026 · five deals open
Black Friday at Mobile Hacking Lab.
Mobile exploit training from the team that placed 3rd overall at Pwn2Own Ireland 2026. Five deals, from €500 and up to 61% off. Enroll now, start whenever you want.
Short videos from the courses in these deals. They load from YouTube when you press play.
Android Userland Fuzzing & Exploitation: the trailer
Enroll once. Keep it.
Buy at the Black Friday price. Start whenever you want.
Black Friday is the cheapest moment to enroll, not a deadline to start studying. This holds for every deal on this page.
Enroll now, start anytime
Enrolling locks in the price. There is no start date: begin next week, or when your current project is done.
Lifetime access
One payment, no subscription. The course content stays in your account for good.
Every update included
New sections and updated material are added to your account as we release them, at no extra cost.
Unlimited exam attempts
Every certification is a hands-on practical exam. If you do not pass the first time, take it again.
Cloud labs, nothing to install
Lab devices and VMs run in your browser, real iPhones included. No Mac, no phone, no hardware to buy.
From the research community
What researchers say after taking these courses.
Reviews of the Android Userland and Kernel courses and of the CAPT exam.
“The Android UserLand Fuzzing And Exploitation Course was an excellent way to deepen my knowledge, the course ranges from basic concepts to much more advanced exploitation topics. The course has many exercises to delve into topics related to reverse engineering, fuzzing and vulnerability exploitation. Anyone who wants to learn or delve deeper into topics related to this fascinating world can start with this course.”
Android Userland Fuzzing and Exploitation
“An excellent way to build solid, practical expertise in vulnerability research and exploit development. It progresses from core fundamentals to advanced topics, with a strong focus on turning discovered bugs into real exploitation scenarios. The course develops practical capabilities in crash analysis, reverse engineering, memory corruption, and exploitation. Highly recommended for anyone looking to deepen their understanding of Android security and modern exploitation techniques.”
Android Kernel Fuzzing and Exploitation
“The CAPT exam is a rigorous and cutting-edge challenge that thoroughly tested my Android userspace bug-hunting methodology. The training materials provided an excellent exercise in identifying Android OS-specific vulnerabilities, combining both static and dynamic code analysis. The focus on real-world issues — web applications and dependency vulnerabilities — made it not just theoretical but truly practical.”
CAPT exam and Android Application Security
“Android Userland Fuzzing and Exploitation course offers a great way to transition from logic bug to memory corruption bug within Android userland application. The lab exercises and the Corellium device provide a user-friendly platform to practice and experiment with the newly acquired skills. The exam allows to use real-world methodologies from fuzzing, crash analysis, and exploiting vulnerabilities to achieve remote code execution.”
Android Userland Fuzzing and Exploitation
“The Android Kernel Fuzzing and Exploitation course delivered everything I needed. It covers fuzzing-based vulnerability discovery through to debugging and developing a final exploit in a Linux kernel environment, complemented by hands-on learning with QEMU and Corellium. The Mobile Hacking Lab support team was always responsive and helpful. This course gave me a strong foundation in vulnerability research that extends well beyond Android — valuable for anyone working with the Linux kernel in any context.”
Android Kernel Fuzzing and Exploitation
“The Mobile Hacking Lab's Android Userland Fuzzing and Exploitation course will take someone with limited background in vulnerability discovery to exploiting a live system with a reverse shell. They have tons of labs and short digestible videos. The instructors are very approachable. The use of Corellium provides hands-on experience during the lab and the exam. Everything you need to pass the exam is taught in the class.”
Android Userland Fuzzing and Exploitation
“This course picks up where the Userland course leaves off. Kernel emulation, internals, memory management and drivers are covered in detail. Production-grade Syzkaller fuzzing for both black and white box approaches. Exploitation techniques such as Dirty Pipe, Pagetable Stack and Heap Overflows, Use-After-Free, and Double-Free are fully explained in brain-melting detail. Writeups, walkthrough videos and working solutions to recreate and follow along. A challenging and rewarding experience.”
Android Kernel Fuzzing and Exploitation
“I took the Android Userland Fuzzing and Exploitation course to improve my Android security skills. It was a success beyond my expectations! From arm64 architecture to fuzzing and finally exploitation, the course combines theory and practical labs through videos and detailed courses. The instructors are always on hand to provide explanations and technical support. What I liked most was the realistic case studies, which can be applied to real-life situations and future research.”
Android Userland Fuzzing and Exploitation
“The Android Kernel Exploitation course and exam were exceptional, challenging, and genuinely fun from fuzzing all the way through to a working LPE. The material gave me everything I needed to go from a crash to a full root exploit and the exam was polished with zero friction. Easily some of the best hands on kernel content I've done.”
Android Kernel Fuzzing and Exploitation
“The Android Userland Fuzzing and Exploitation course at Mobile Hacking Lab offers a solid, practical look at userland security on Android. It covers everything from basic stack buffer overflows to more advanced heap spraying and exploitation on ARM, bypassing restrictions such as ASLR. The hands-on tasks are an amazing touch, and it is a really good fit for those who want a real-world introduction to Android exploitation techniques.”
Android Userland Fuzzing and Exploitation
“This is without a doubt, the best Android kernel exploitation course I've come across. The course provides an in-depth understanding of kernel exploitation primitives, modern exploit mitigations, and the techniques used to bypass them. What really sets it apart is its focus on real-world exploitation, with actual CVEs thoroughly explained through both video demonstrations and written material. […]”
Android Kernel Fuzzing and Exploitation
“The Android UserLand Fuzzing And Exploitation Course was an excellent way to deepen my knowledge, the course ranges from basic concepts to much more advanced exploitation topics. The course has many exercises to delve into topics related to reverse engineering, fuzzing and vulnerability exploitation. Anyone who wants to learn or delve deeper into topics related to this fascinating world can start with this course.”
Android Userland Fuzzing and Exploitation
“An excellent way to build solid, practical expertise in vulnerability research and exploit development. It progresses from core fundamentals to advanced topics, with a strong focus on turning discovered bugs into real exploitation scenarios. The course develops practical capabilities in crash analysis, reverse engineering, memory corruption, and exploitation. Highly recommended for anyone looking to deepen their understanding of Android security and modern exploitation techniques.”
Android Kernel Fuzzing and Exploitation
“The CAPT exam is a rigorous and cutting-edge challenge that thoroughly tested my Android userspace bug-hunting methodology. The training materials provided an excellent exercise in identifying Android OS-specific vulnerabilities, combining both static and dynamic code analysis. The focus on real-world issues — web applications and dependency vulnerabilities — made it not just theoretical but truly practical.”
CAPT exam and Android Application Security
“Android Userland Fuzzing and Exploitation course offers a great way to transition from logic bug to memory corruption bug within Android userland application. The lab exercises and the Corellium device provide a user-friendly platform to practice and experiment with the newly acquired skills. The exam allows to use real-world methodologies from fuzzing, crash analysis, and exploiting vulnerabilities to achieve remote code execution.”
Android Userland Fuzzing and Exploitation
“The Android Kernel Fuzzing and Exploitation course delivered everything I needed. It covers fuzzing-based vulnerability discovery through to debugging and developing a final exploit in a Linux kernel environment, complemented by hands-on learning with QEMU and Corellium. The Mobile Hacking Lab support team was always responsive and helpful. This course gave me a strong foundation in vulnerability research that extends well beyond Android — valuable for anyone working with the Linux kernel in any context.”
Android Kernel Fuzzing and Exploitation
“The Mobile Hacking Lab's Android Userland Fuzzing and Exploitation course will take someone with limited background in vulnerability discovery to exploiting a live system with a reverse shell. They have tons of labs and short digestible videos. The instructors are very approachable. The use of Corellium provides hands-on experience during the lab and the exam. Everything you need to pass the exam is taught in the class.”
Android Userland Fuzzing and Exploitation
“This course picks up where the Userland course leaves off. Kernel emulation, internals, memory management and drivers are covered in detail. Production-grade Syzkaller fuzzing for both black and white box approaches. Exploitation techniques such as Dirty Pipe, Pagetable Stack and Heap Overflows, Use-After-Free, and Double-Free are fully explained in brain-melting detail. Writeups, walkthrough videos and working solutions to recreate and follow along. A challenging and rewarding experience.”
Android Kernel Fuzzing and Exploitation
“I took the Android Userland Fuzzing and Exploitation course to improve my Android security skills. It was a success beyond my expectations! From arm64 architecture to fuzzing and finally exploitation, the course combines theory and practical labs through videos and detailed courses. The instructors are always on hand to provide explanations and technical support. What I liked most was the realistic case studies, which can be applied to real-life situations and future research.”
Android Userland Fuzzing and Exploitation
“The Android Kernel Exploitation course and exam were exceptional, challenging, and genuinely fun from fuzzing all the way through to a working LPE. The material gave me everything I needed to go from a crash to a full root exploit and the exam was polished with zero friction. Easily some of the best hands on kernel content I've done.”
Android Kernel Fuzzing and Exploitation
“The Android Userland Fuzzing and Exploitation course at Mobile Hacking Lab offers a solid, practical look at userland security on Android. It covers everything from basic stack buffer overflows to more advanced heap spraying and exploitation on ARM, bypassing restrictions such as ASLR. The hands-on tasks are an amazing touch, and it is a really good fit for those who want a real-world introduction to Android exploitation techniques.”
Android Userland Fuzzing and Exploitation
“This is without a doubt, the best Android kernel exploitation course I've come across. The course provides an in-depth understanding of kernel exploitation primitives, modern exploit mitigations, and the techniques used to bypass them. What really sets it apart is its focus on real-world exploitation, with actual CVEs thoroughly explained through both video demonstrations and written material. […]”
Android Kernel Fuzzing and Exploitation
“Android Userland Fuzzing and Exploitation is an excellent course for security researchers looking to dive into Android app exploitation. It provides comprehensive coverage of essential topics, from the Android security model and AArch64 reverse engineering to fuzzing, stack buffer overflows, and practical Android-specific heap exploitation techniques with real-world CVE analysis.”
Android Userland Fuzzing and Exploitation
“The Android UserLand Fuzzing and Exploitation Course has been an incredible resource. It covers everything from the basics to more advanced exploitation techniques, making it suitable for all levels. The hands-on exercises were especially helpful in diving deep into reverse engineering, fuzzing, and vulnerability exploitation. The one-on-one support calls and labs after each section helped clarify concepts and gave me practical insight.”
Android Userland Fuzzing and Exploitation
“From arm64 architecture to fuzzing and finally exploitation, the course combines theory and practical labs through videos and detailed courses. The instructors are always on hand to provide explanations and technical support. The realistic case studies can be applied to real-life situations and future research.”
Android Userland Fuzzing and Exploitation
“Having recently completed this course, I can confidently say it's a game-changer. The course offers hands-on learning with real-world applications, covering everything from Android basics to advanced exploitation. The instructors are experts in their field, and the support staff are incredibly helpful. The gamified approach to learning makes it both enjoyable and intellectually stimulating.”
Android Userland Fuzzing and Exploitation
“Mobile Hacking Lab covers everything you need to know about low-level Android reverse engineering, vulnerability research, fuzzing, and exploitation. The best part is that the course is 100% hands-on with real-world applications. There's no other course like it out there. Highly recommended!”
Android Userland Fuzzing and Exploitation
“Joining this course was a fun game-changer for me. It provided a deep dive into Android security, from Android basics to advanced exploitation, all through a practical, hands-on learning experience. The tasks were intriguing and came with engaging challenges. I recommend it to everyone interested in the Android operating system.”
Android Userland Fuzzing and Exploitation
“The mobile hacking training at Mobile Hacking Lab not only boosted my skills in fuzzing and exploitation but also impressed me with their very supportive and kind staff. Highly recommend!”
Android Userland Fuzzing and Exploitation
“Upon diving into this course with the goal of becoming a Certified Android Exploit Developer, I've learned many things throughout the process. As a hands-on learner, the materials offered throughout the course were an absolute game changer. The overall experience was fantastic and definitely full of a roller coaster of emotion.”
Android Userland Fuzzing and Exploitation
“The Android Userland Fuzzing and Exploitation course is everything as advertised. A practical hands-on deep dive on fuzzing for white and black box testing. Step-by-step reverse engineering, a primer for ARM assembly, and a detailed walkthrough of how info leaks can lead to full remote code execution, NX and ASLR bypass, and modern heap exploitation. The MHL team was amazing in their support.”
Android Userland Fuzzing and Exploitation
“This training took me from zero to writing a complete ASLR-bypass exploit for Android. The hands-on approach of working through real vulnerabilities — heap overflows, jemalloc internals, and libc leaks — taught me more than any textbook ever could. Highly recommended for anyone serious about mobile security.”
Android Userland Fuzzing and Exploitation
“The Android Userland Fuzzing and Exploitation course by MobileHackingLab is an excellent introduction to Android userland components and the techniques used to fuzz and exploit them. The course provides a valuable foundation in an area where comparable training opportunities are currently limited. I would highly recommend it to researchers looking to build or strengthen their skills in Android security.”
Android Userland Fuzzing and Exploitation
“Android Userland Fuzzing and Exploitation is an excellent course for security researchers looking to dive into Android app exploitation. It provides comprehensive coverage of essential topics, from the Android security model and AArch64 reverse engineering to fuzzing, stack buffer overflows, and practical Android-specific heap exploitation techniques with real-world CVE analysis.”
Android Userland Fuzzing and Exploitation
“The Android UserLand Fuzzing and Exploitation Course has been an incredible resource. It covers everything from the basics to more advanced exploitation techniques, making it suitable for all levels. The hands-on exercises were especially helpful in diving deep into reverse engineering, fuzzing, and vulnerability exploitation. The one-on-one support calls and labs after each section helped clarify concepts and gave me practical insight.”
Android Userland Fuzzing and Exploitation
“From arm64 architecture to fuzzing and finally exploitation, the course combines theory and practical labs through videos and detailed courses. The instructors are always on hand to provide explanations and technical support. The realistic case studies can be applied to real-life situations and future research.”
Android Userland Fuzzing and Exploitation
“Having recently completed this course, I can confidently say it's a game-changer. The course offers hands-on learning with real-world applications, covering everything from Android basics to advanced exploitation. The instructors are experts in their field, and the support staff are incredibly helpful. The gamified approach to learning makes it both enjoyable and intellectually stimulating.”
Android Userland Fuzzing and Exploitation
“Mobile Hacking Lab covers everything you need to know about low-level Android reverse engineering, vulnerability research, fuzzing, and exploitation. The best part is that the course is 100% hands-on with real-world applications. There's no other course like it out there. Highly recommended!”
Android Userland Fuzzing and Exploitation
“Joining this course was a fun game-changer for me. It provided a deep dive into Android security, from Android basics to advanced exploitation, all through a practical, hands-on learning experience. The tasks were intriguing and came with engaging challenges. I recommend it to everyone interested in the Android operating system.”
Android Userland Fuzzing and Exploitation
“The mobile hacking training at Mobile Hacking Lab not only boosted my skills in fuzzing and exploitation but also impressed me with their very supportive and kind staff. Highly recommend!”
Android Userland Fuzzing and Exploitation
“Upon diving into this course with the goal of becoming a Certified Android Exploit Developer, I've learned many things throughout the process. As a hands-on learner, the materials offered throughout the course were an absolute game changer. The overall experience was fantastic and definitely full of a roller coaster of emotion.”
Android Userland Fuzzing and Exploitation
“The Android Userland Fuzzing and Exploitation course is everything as advertised. A practical hands-on deep dive on fuzzing for white and black box testing. Step-by-step reverse engineering, a primer for ARM assembly, and a detailed walkthrough of how info leaks can lead to full remote code execution, NX and ASLR bypass, and modern heap exploitation. The MHL team was amazing in their support.”
Android Userland Fuzzing and Exploitation
“This training took me from zero to writing a complete ASLR-bypass exploit for Android. The hands-on approach of working through real vulnerabilities — heap overflows, jemalloc internals, and libc leaks — taught me more than any textbook ever could. Highly recommended for anyone serious about mobile security.”
Android Userland Fuzzing and Exploitation
“The Android Userland Fuzzing and Exploitation course by MobileHackingLab is an excellent introduction to Android userland components and the techniques used to fuzz and exploit them. The course provides a valuable foundation in an area where comparable training opportunities are currently limited. I would highly recommend it to researchers looking to build or strengthen their skills in Android security.”
Android Userland Fuzzing and Exploitation
Reviews as published on mobilehackinglab.com. Each card names the course it is about.
Who is teaching you
Built by researchers who do this for a living.
3rd overall
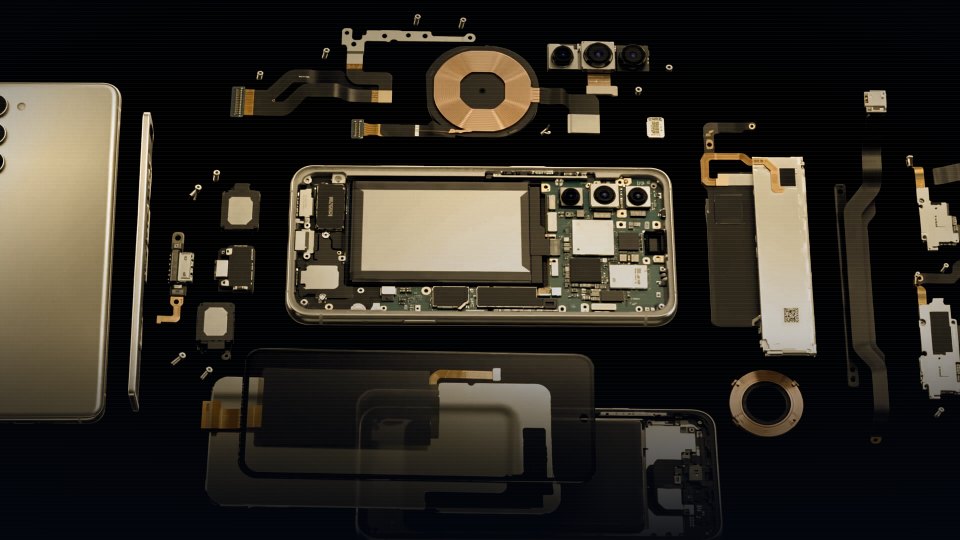
The Mobile Hacking Lab research team placed 3rd overall at Pwn2Own Ireland 2026, with working exploits for the Samsung Galaxy S26 and the Google Pixel 10.
Questions
Before you enroll.
Can I enroll now and start later?
Yes. Enrolling locks in the Black Friday price. There is no start date, and because access to the content is for life there is no date you have to finish by.
How long do I keep access?
For life. Every deal is a one-time payment, not a subscription. The course content stays in your account, including the updates we add later. Lab access is set per course and described on each deal page.
How many exam attempts do I get?
Unlimited. If you do not pass a practical exam the first time, you can take it again at no extra cost.
What do I need to run the labs?
A laptop with a modern browser. The lab devices and VMs are hosted by us. You do not need a Mac or a phone.
Can my employer pay by invoice or purchase order?
Yes. Email hello@mobilehackinglab.com with the deal and your company details and we send an invoice at the Black Friday price, as long as the request arrives before the sale ends.
When do these prices end?
The bundle prices end on Monday 30 November at 23:59 CET. The iOS WebKit presale price rises earlier: it steps up every week until the course is released.
Black Friday 2026
5 deals. From €500.
Black Friday ends in
See the deals →
Enroll now. Start anytime. Keep it for life. · Invoice or purchase order: hello@mobilehackinglab.com
From €5005 Black Friday deals · up to 61% offends in
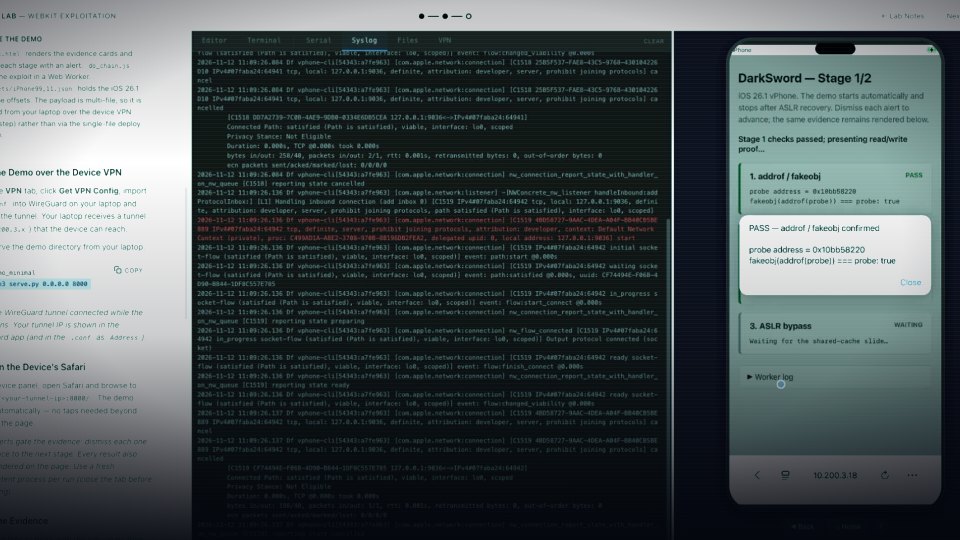 iOS WebKit Exploitation on ARM64
 Android Kernel + Userland
 Full Chain iOS
 Full Chain Android
 59% off
 Android Userland Fuzzing & Exploitation: the trailer