Black Friday presale  ·  iOS WebKit Exploitation at €800 instead of €2,000  ·  price goes up in
New course · Black Friday presale

One JavaScript bug.
A full iOS exploit chain.

Fuzz JavaScriptCore, build addrof/fakeobj and arbitrary read/write, bypass PAC, then rebuild the in-the-wild DarkSword chain on a real iPhone running iOS 26.1.

Black Friday presale€800€2,000price goes up in
13Hands-on sections
6 CVEsThe DarkSword chain
iOS 26.1Real iPhones in your browser
30,000+Learners on the platform

Trusted by security teams at
GoogleAdobeRevolutDark WolfNordVPNNCC GroupCensus LabsEYDeloittePwCABN AMROGroup-IB
What you will build

DarkSword: an in-the-wild iOS chain, rebuilt stage by stage.

Documented by Google Threat Intelligence Group after it was used by surveillance vendors and state-sponsored actors, DarkSword compromises iOS 18.4 to 18.7 with six vulnerabilities. The course works up to it from JavaScriptCore fundamentals.

On iOS 26.1 the renderer RCE, the PAC bypass and the WebContent escape are still reproducible hands-on. The two kernel-side stages were patched in 26.1 and are covered through patch analysis.

The lab

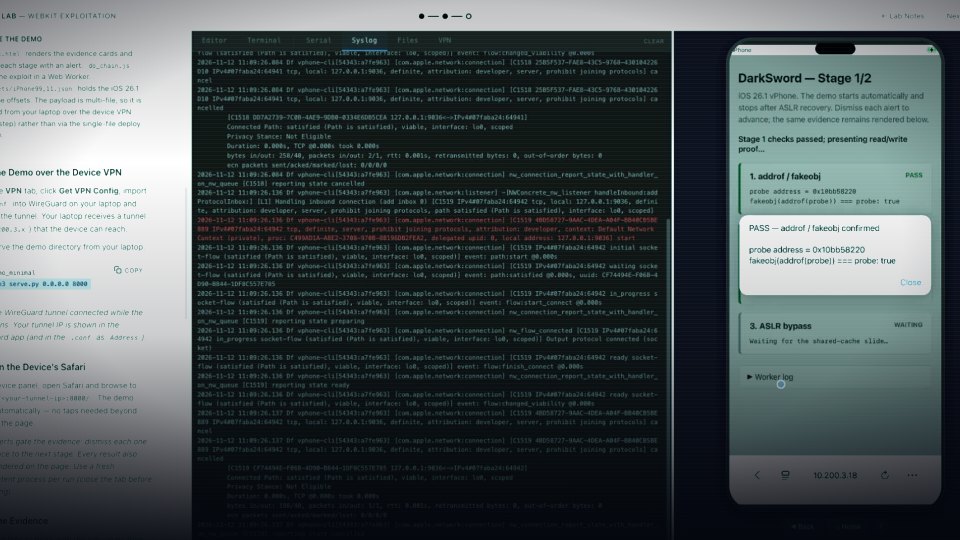
This is the lab. It runs in your browser.

Guided notes on the left, a live terminal in the middle, a real iPhone on the right. The recording shows the DarkSword stage 1 and 2 lab running against a Device Lab iPhone on iOS 26.1.

Lab 10.1 · DarkSword stage 1 and 2 · Real iOS 26.1 Device Lab iPhone
A dedicated ARM64 Ubuntu VM with JavaScriptCore debug, release and ASAN builds
LLDB, Frida, pwntools and Fuzzilli pre-installed
Real iPhones on iOS 26.1 for the full-chain and exam labs
Nothing to install. No Mac or iPhone required
Curriculum

13 sections. Every one has labs.

The first sections are live now. The rest is released over the coming weeks, and you get each one as it ships.

PART 1

Foundations, Bug Classes & Fuzzing

Build and debug JavaScriptCore from source, master the object model and JIT tiers, trigger every major WebKit bug class, dissect five real CVEs under ASAN, and run coverage-guided Fuzzilli campaigns against JSC.

01WebKit Architecture & Debugging Fundamentals7 lessons
  • 1.1 WebKit architecture: WebCore, JavaScriptCore, and the WebKit2 multi-process model
  • 1.1 The rendering pipeline: HTML parsing → DOM → layout → paint → compositing
  • 1.1 Build the JSC debug build from source on ARM64 and verify the toolchain
  • 1.2 Release vs debug builds: $vm, describe(), and explicit GC control
  • 1.2 Inspect JSObject internals with describe() and $vm
  • 1.3 Debugging flags: --useConcurrentJIT=false, --dumpGeneratedBytecodes=true
  • 1.3 LLDB on JSC: breakpoints, watchpoints, crash logs, and ASAN reports
02JavaScriptCore Deep Dive7 lessons
  • 2.1 Execution tiers: LLInt → Baseline JIT → DFG JIT → FTL JIT
  • 2.1 Speculative optimization, type feedback, and on-stack replacement (OSR)
  • 2.1 Observe tier-up and force DFG/FTL compilation
  • 2.2 JSValue and NaN-boxing; JSCell, JSObject, Structure, and Butterfly
  • 2.2 Heap layout and cell allocation: MarkedBlock and LargeAllocation
  • 2.2 Riptide GC: concurrent, generational mark-sweep; write barriers
  • 2.2 Drive gc(), fullGC(), and edenGC() to control object lifetimes
03Common WebKit Bug Categories7 lessons
  • 3.1 Type confusion: Structure IDs and speculated types in DFG/FTL
  • 3.1 Classic case study: CVE-2016-4622 property type confusion
  • 3.1 Trigger a type confusion via Structure ID reuse
  • 3.2 Use-after-free: GC-related UAFs, DOM lifecycle bugs, zombie objects
  • 3.2 Trigger a UAF via GC timing manipulation
  • 3.3 Out-of-bounds: range analysis, bounds-check hoisting, integer overflow in index math
  • 3.3 Trigger an OOB access via JIT bounds-check elimination
04Real-World CVE Deep Dives9 lessons
  • 4.1 CVE-2022-32893: OOB write in WebCore via counter length mismatch
  • 4.1 Trigger CVE-2022-32893 in an ASAN-instrumented build
  • 4.2 CVE-2023-28205: C++/JS garbage-collector lifetime disagreement in the DOM
  • 4.2 Trigger CVE-2023-28205 in an ASAN build
  • 4.3 CVE-2023-32373: re-entrancy UAF during layout in the rendering pipeline
  • 4.3 Trigger CVE-2023-32373 in an ASAN build
  • 4.4 CVE-2023-42917: memory corruption; analysis from patch diffing
  • 4.5 CVE-2024-23222: DFG JIT type confusion leading to addrof/fakeobj
  • 4.5 Trigger the CVE-2024-23222 type confusion in an ASAN build
05Fuzzing7 lessons
  • 5.1 JS-engine fuzzing fundamentals: generation vs mutation, coverage guidance
  • 5.1 Differential testing: optimized vs unoptimized, cross-engine diffs against V8/SpiderMonkey
  • 5.2 Fuzzilli: the FuzzIL intermediate representation, program-level mutations, REPRL mode
  • 5.2 Other engine fuzzers: Dharma, CodeAlchemist, and where they fit
  • 5.2 Build Fuzzilli and run a coverage-guided campaign against JSC + ASAN
  • 5.3 Crash triage: deduplication, bucketing, exploitability assessment, minimization
  • 5.3 Minimize a real fuzzer crash to a clean PoC and root-cause it
PART 2

Exploitation, Mitigations & Sandboxes

Turn bugs into primitives and primitives into code execution. Work around Gigacage, IsoHeap, the JIT cage and PAC, then map the renderer attack surface on both iOS and Android.

06Exploitation Primitives5 lessons
  • 6.1 addrof and fakeobj: the foundation of every JSC exploit
  • 6.1 Implement addrof/fakeobj from a type confusion bug
  • 6.2 A fake Float64Array with a controlled backing store → arbitrary R/W
  • 6.2 Defeating ASLR by reading known structure layouts
  • 6.2 Build a stable arbitrary R/W and read JSC heap metadata
07Control Flow Hijacking5 lessons
  • 7.1 The JIT code region: RWX → RX, and how to write JIT shellcode
  • 7.1 ARM64 instruction encoding and icache coherency considerations
  • 7.1 JIT code overwrite: code execution from arbitrary R/W
  • 7.2 ROP on AArch64: gadgets, stack pivoting, calling conventions
  • 7.2 Build an ARM64 ROP chain against WebKit
08WebKit Mitigations5 lessons
  • 8.1 Gigacage, IsoHeap, Structure ID randomization, and the JIT cage
  • 8.2 Hardware mitigations: PAC, APRR/PPL, SPTM, MTE; KTRR and KPP
  • 8.3 Bypass techniques: Gigacage and Structure ID bypasses, data-only attacks, WASM corruption
  • 8.3 Case study: CVE-2026-20700, the dyld PAC bypass used by DarkSword
  • 8.1 Mitigation inventory: identify the bypass surface on the lab targets
09iOS WebKit Sandbox5 lessons
  • 9.1 WebKit on iOS: the only permitted engine; WKWebView vs UIWebView
  • 9.2 The WebContent Seatbelt profile: com.apple.WebProcess.sb
  • 9.2 Dissect the sandbox profile (permitted syscalls and Mach services)
  • 9.3 Renderer-to-browser attack surface: Mach IPC and sandbox-escape vectors
  • 9.3 Enumerate and analyze reachable Mach services
10Android Chrome Sandbox4 lessons
  • 10.1 V8 vs JSC: different engine, same bug classes; Chrome’s process model; WebView
  • 10.2 The renderer sandbox: seccomp-bpf, SELinux, namespaces; Mojo IPC; site isolation
  • 10.2 Inspect Chrome’s sandbox (seccomp filters, SELinux policy, Mojo endpoints)
  • 10.3 iOS vs Android: PAC vs MTE, sandbox profiles vs seccomp, post-exploitation paths
PART 3

The DarkSword Chain: Full iOS N-Day Exploitation

Reconstruct the in-the-wild DarkSword iOS chain stage by stage on iOS 26.1 Device Lab iPhones: renderer RCE, the dyld PAC bypass, both sandbox escapes, and the kernel stages via patch analysis.

11Full N-Day Chain: DarkSword11 lessons
  • 11.1 Threat landscape: UNC6748, PARS Defense, UNC6353; delivery, loaders, Web Worker architecture
  • 11.2 Stage 1 (Renderer RCE): CVE-2025-31277 & CVE-2025-43529 in JavaScriptCore
  • 11.2 Reproduce the RCE on an iOS 26.1 device → fakeobj/addrof → arbitrary R/W
  • 11.3 Stage 2 (PAC bypass): CVE-2026-20700 in dyld
  • 11.3 Weaponize the dyld PAC bypass for code execution under PAC
  • 11.4 Stage 3 (WebContent escape): CVE-2025-14174, the ANGLE WebGL bug that reaches the GPU process
  • 11.4 Escape the WebContent sandbox into the GPU process
  • 11.5 Stage 4 (GPU escape): CVE-2025-43510, the XNU copy-on-write bug that reaches mediaplaybackd
  • 11.6 Stage 5 (Kernel LPE): CVE-2025-43520, the XNU VFS race for kernel physical/virtual R/W
  • 11.6 Patch-diff the kernel stages and walk the full chain end to end
  • 11.7 Post-exploitation: TaskRop, MigFilterBypass; GHOSTBLADE / GHOSTKNIFE / GHOSTSABER payloads
PART 4

AI-Guided Vulnerability Research

A standalone module on AI-assisted vulnerability research: agentic workflows plus MHL’s free custom fine-tuned WebKit LLM for code audit, crash triage, patch-diffing, and exploit scaffolding, all verified against the debugger.

12AI-Guided Vulnerability Research5 lessons
  • 12.1 Agentic VR workflows: code audit, crash triage, patch-diffing, exploit scaffolding
  • 12.1 Validation discipline: confirming agent output against ASAN and the debugger
  • 12.1 AI-agent pipeline from fuzzing crash to root-cause write-up and minimal trigger
  • 12.2 MHL’s fine-tuned WebKit LLM: trained on WebKit source, CVE write-ups, patch diffs
  • 12.2 Run the fine-tuned LLM on a JSC subsystem, rank bug hypotheses, validate the top candidate
PART 5

The Final Exam

Prove everything in a time-boxed practical exam on an unseen target: triage, root cause, primitives, code execution, with a bonus browser-delivery objective on a real iPhone.

13Final Hands-On Exam5 lessons
  • 13.1 Unseen target: a minimized JSC crash or a patch to reverse, on a fixed vulnerable build
  • 13.1 Full kill chain in the JSC shell: triage → root cause → primitives → code execution
  • 13.2 Open-book: course material and AI tooling permitted, with documented verification
  • 13.3 Graded on root-cause analysis, primitive reliability, code execution, and report quality
  • 13.3 Bonus objective: browser delivery to Safari on an iOS 26.1 Device Lab iPhone
What is included

Everything from your first JSC build to a full chain.

ARM64 Lab VM in Browser

A dedicated AArch64 Ubuntu 24.04 VM with JavaScriptCore debug & release builds and WebKitGTK for browser-context labs. Start debugging JSC within minutes.

Real iOS 26.1 iPhones

Full-chain and exam labs run on Mobile Hacking Lab Device Lab iPhones. Serve your exploit to Safari and watch it execute on real hardware.

Fuzzilli Fuzzing Infrastructure

Coverage-guided Fuzzilli campaigns against ASAN-instrumented JSC builds, with REPRL in-process mode, crash dedup, and minimization workflows.

Five Real CVEs, Interactive Labs

CVE-2022-32893, CVE-2023-28205, CVE-2023-32373, CVE-2023-42917 and CVE-2024-23222, each with root cause analysis, patch review, and an ASAN lab.

Free Custom WebKit LLM

Our own small language model, fine-tuned on WebKit/JSC source, CVE write-ups and patch diffs. Free with the course, plus agentic workflows for triage and exploit scaffolding.

Hands-On Final Exam

A time-boxed practical on an unseen target: triage → root cause → addrof/fakeobj → arbitrary R/W → code execution. Bonus: browser delivery on a real iPhone.

Enroll once. Keep it.

Buy at the presale price. Start whenever you want.

Black Friday is the cheapest moment to enroll, not a deadline to start studying. Everything below is included in the one-time price.

Enroll now, start anytime

Enrolling locks in today's price. There is no start date: begin next week, or when your current project is done.

Lifetime access

One payment, no subscription. The course stays in your account for good, so you can work through it at your own pace and come back to it later.

Every update included

New sections and updated material are added to your account as we release them, at no extra cost.

Unlimited exam attempts

The course ends with a hands-on practical exam. If you do not pass the first time, take it again. And again.

Cloud labs with real devices

A cloud ARM64 VM and device access to real iPhones on iOS 26.1, in your browser, to complete every lab. No Mac or iPhone of your own needed.

Who is teaching you

Built by researchers who do this for a living.

3rd overall

The Mobile Hacking Lab research team placed 3rd overall at Pwn2Own Ireland 2026, with working exploits for the Samsung Galaxy S26 and the Google Pixel 10. The same team builds and maintains these labs.

Presale pricing

The price rises every week until release.

The course is in presale while the last sections are released. Each week the price steps up towards the regular price. Today's price is the lowest it will be again.

Until Mon 16 Nov€600

First presale step. Ended.

Today€800

Black Friday presale. 60% off the regular price.

Enroll at this price →

At full release€2,000

The regular price of the course.

Black Friday presale

Everything, for €800 instead of €2,000.

One payment. No subscription. Enroll today and start when it suits you.

  • The full course: 13 hands-on sections, from JavaScriptCore internals to a full iOS chain
  • Cloud labs: an ARM64 VM and device access to real iPhones on iOS 26.1
  • The DarkSword chain, rebuilt stage by stage on real devices
  • The fine-tuned WebKit LLM, free with the course
  • Hands-on final exam with unlimited attempts
  • Lifetime access and every future update
  • Enroll now, start anytime
Black Friday presaleSave €1,200 · 60% off
€800€2,000

One-time payment. Lifetime access. Start anytime.

Price goes up Mon 23 Nov, 12:00 CET

--Days
--Hours
--Min
--Sec
Enroll for €800 →

Secure checkout by card, iDEAL, Klarna and more. Company invoice: hello@mobilehackinglab.com

Black Friday bundle

Or take the whole iOS chain: browser to 0-click.

WebKit gets you code execution from a web page. iOS Userland takes you into 0-click territory: fuzzing ImageIO, CoreText and CoreAudio, and a 3-stage 0-click against a messaging app. The bundle adds the CIPT certification.
Course 1 · Browser

WebKit Exploitation on ARM64

13 sections · Device Lab iPhones · final exam
€2,000
Course 2 · 0-click

iOS Userland Fuzzing & Exploitation

60 hours · 90-day lab · CIED

€2,500
Certification

CIPT, Certified iOS Penetration Tester

72-hour practical exam

€249
Black Friday bundleSave €2,750 · 58% off
€1,999€4,749

Both courses and the certification. One payment, lifetime access, start anytime.

Get the bundle →
  • iOS Userland alone is €2,500
  • Unlimited exam attempts for CIED and CIPT
  • Cloud labs with real iPhones and a cloud VM
  • Enroll now, start anytime

Already have one of these courses?

Then you should not pay for it twice. Email us which course you own and we will make you a personal offer for the rest of the bundle.
Ask for my personal offer →
More Black Friday deals

On the Android side? Two more deals.

Entry ticket · last year's best seller

Advanced AppSec Bundle

Advanced Android Hacking with a 3x Pwn2Own winner, plus the CAPT and CIPT certifications.

€500€1,208

Save €708 · 59% off

One course, three certifications

See the bundle →
Android · 0-click to ring 0

Android Kernel + Userland

Two courses and two certifications: from a fuzzer crash in a messaging parser to root in the kernel.

€1,799€4,574

Save €2,775 · 61% off

Less than the Kernel course alone

See the bundle →
Questions

Before you enroll.

Can I enroll now and start later?

Yes. Enrolling locks in today's price. There is no start date, and because access is for life there is no date you have to finish by. Many students enroll during a sale and start when their schedule allows.

How long do I keep access?

For life. It is a one-time payment, not a subscription. The course stays in your account, including the sections and updates we add later.

How many exam attempts do I get?

Unlimited. If you do not pass the hands-on final exam the first time, you can take it again at no extra cost.

The course is in presale. What is available today?

The first sections are live now and the remaining sections are released over the coming weeks, together with the fine-tuned WebKit LLM. You get each section as it ships.

Will the price really go up?

Yes. The presale price rises every week until the full course is released, when it becomes €2,000. It was €600 until Monday 16 November and it is €800 now.

What do I need to run the labs?

A laptop with a modern browser. The ARM64 cloud VM and the device access to real iPhones on iOS 26.1 that you need to complete the labs are included. You do not need a Mac or an iPhone.

What background do I need before starting?

C/C++ programming experience, JavaScript proficiency, a basic understanding of memory management and CPU architecture, and Linux command-line fluency. No prior browser-exploitation experience is required. The course builds up from architecture fundamentals.

Is this hands-on or video-based?

Hands-on throughout. Every one of the thirteen sections has labs: building JSC, triggering real CVEs under ASAN, Fuzzilli campaigns, exploit primitives, and the full DarkSword chain on real devices.

Does it really cover an in-the-wild iOS chain?

Yes. Section 11 reconstructs the DarkSword chain documented by Google GTIG: renderer RCE, the dyld PAC bypass, and the ANGLE WebContent escape hands-on on iOS 26.1 devices, with the kernel-side stages (patched in 26.1) covered through patch analysis.

Is the WebKit LLM really free?

Yes. Every enrolled student gets MHL’s custom fine-tuned WebKit LLM at no extra cost. No subscription, no API fees. It runs locally in your lab environment and is yours throughout the course: triaging Fuzzilli crashes in Section 5, auditing JSC subsystems and generating bug hypotheses in Section 12, and even during the final exam (AI usage is allowed, as long as you verify everything in the debugger).

Can my employer pay by invoice or purchase order?

Yes. Email hello@mobilehackinglab.com with the product name and your company details and we send an invoice at this price, as long as the request arrives before the deadline.

Black Friday presale

Lock in €800 before the next price step.

€800€2,000

Price goes up in

Enroll for €800 → Enroll now. Start anytime. Keep it for life.  ·  Invoice or purchase order: hello@mobilehackinglab.com
€800€2,000iOS WebKit Exploitation · Black Friday presalegoes up in
Enroll now →